Reverse Engineering & Code Tampering
Mobile applications contain business logic, security controls, API endpoints, sensitive strings, and implementation details that attackers can analyse after obtaining the application package.
Attackers can reverse engineer APKs and IPAs, extract application logic, modify code, bypass security controls, and repackage applications for distribution.
What Is Reverse Engineering & Code Tampering?
Reverse engineering involves analysing a mobile application's compiled code to understand its logic, functionality, security controls, APIs, and implementation.
Attackers use tools to decompile application packages, inspect DEX files and native libraries, extract strings, analyse application flows, and identify weaknesses that can later be exploited.
Code tampering goes a step further. Attackers modify application code or resources to change application behaviour, disable security controls, introduce malicious functionality, or bypass application restrictions.
Even when an application is securely developed and signed, its distributed binary can become a target for analysis and manipulation.
This makes application hardening, integrity protection, tamper detection, and runtime protection important layers of mobile application security.
Major Threats Associated With Reverse Engineering
How Attackers Decompile, Modify, and Weaponize Mobile Binaries in the Wild
Intellectual Property Theft
Malware Injection and Trojans
APK & IPA Reverse Engineering
Code & Logic Extraction
DEX & Native Library Analysis
Application Repackaging
Code & Resource Tampering
Security Control Bypass
App Spoofing
Static App Patching
Why Is Mobile Application Code Becoming Harder to Protect?
Empirical Findings on Code Protection Deficits and Increasing Reverse Engineering Capabilities
Security Is Still Behind the Risks
34.8% of Finance Apps Lacks code protection
No Anti-tampering Protection
Code Protection Is Not One Control
Reverse Engineering Can Become a Major Business Risk
When Exposure of Proprietary IP and Core Logic Threatens Commercial Survival
When application code can be analysed or modified, attackers may gain insight into proprietary business logic, security mechanisms, API interactions, authentication flows, or controls designed to prevent abuse.
“Can your mobile application remain trustworthy when its binary is in the hands of an attacker?”
Successful reverse engineering and tampering can contribute to:
Security-control bypass
Application cloning and repackaging
Exposure of sensitive application logic
Manipulation of business workflows
API abuse
Fraud and unauthorised transactions
Distribution of repackaged applications on communication channels like WhatsApp for data theft.
Loss of intellectual property
Why Is Application Hardening Important After Development?
Protecting Binaries in Untrusted Environments Against Decompilation and Static Analysis
Mobile application security cannot rely only on secure coding and pre-release testing.
Once an APK or IPA reaches a user's device, attackers can obtain the application binary and analyse it in environments they control. Application hardening makes this analysis and modification more difficult by protecting the code, strings, libraries, and other application components.
Multi-Layer Defense Architecture
Code Hardening
Tamper Detection
Runtime Integrity
Threat Response
Protection should address both static analysis and runtime manipulation.
Application hardening can make reverse engineering more difficult, while runtime controls can help identify whether an application has been modified or is executing in an untrusted environment.
What Bugsmirror MASST Delivers
Unified Binary Hardening, Anti-Tamper Enforcement, Runtime Integrity, and Threat Intelligence
Application Hardening & Anti-Reverse Engineering
Runtime Tampering Detection
Security Testing Before Deployment
Real-Time Threat Visibility
Strengthen Your Mobile App Against Reverse Engineering
Empowering leading enterprises to protect their digital assets with next-generation security.







Let's Talk Security
Fill out the form below and our security experts will reach out to you shortly.
FAQs
Explore related content
Learn about mobile app protection, anti-reverse engineering, RASP, and app shielding.

How to Prevent Reverse Engineering in Android and iOS Mobile Apps
App repackaging and reverse engineering allow attackers to modify apps, steal data, and clone features. This blog explains how code encryption and app shielding protect mobile applications from tampering and IP theft.
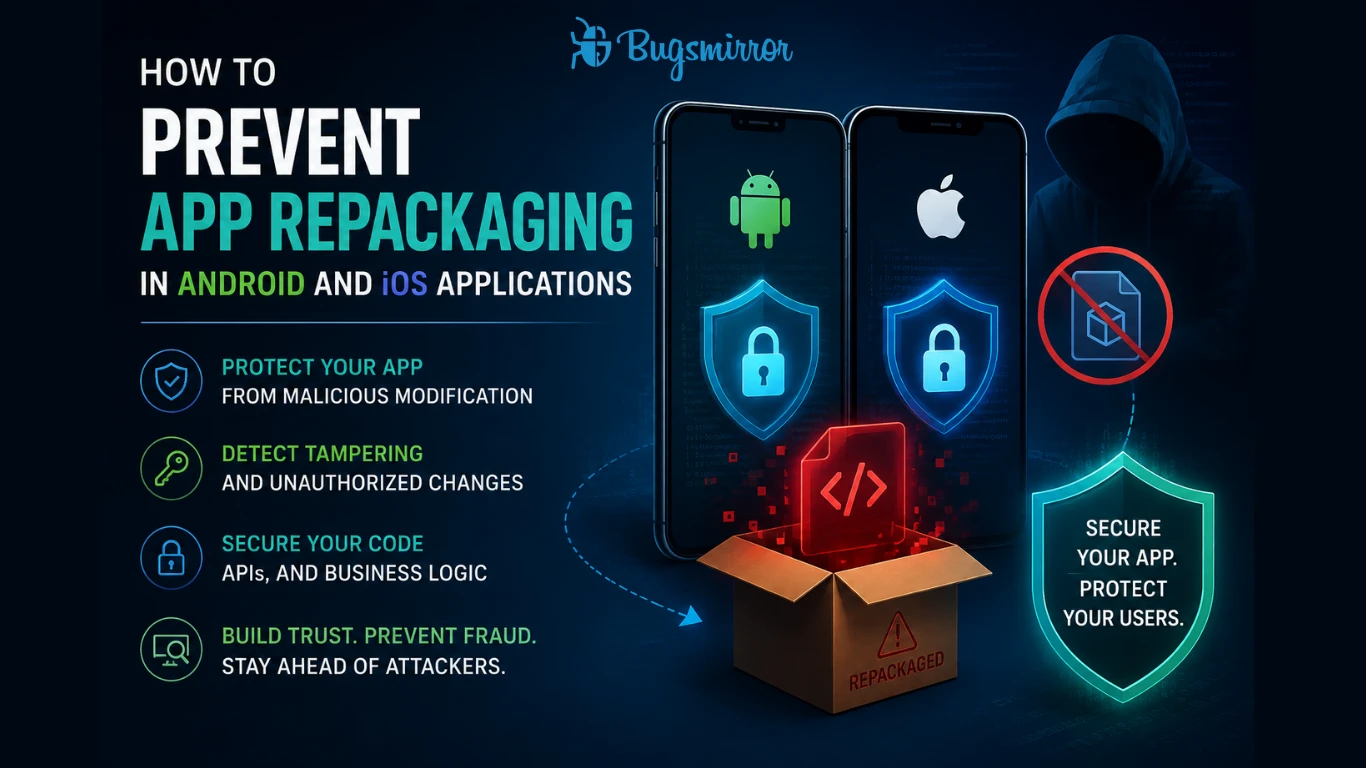
How to Prevent App Repackaging in Android and iOS Applications
App repackaging is a critical mobile app security threat where attackers modify and redistribute legitimate apps to inject malicious code. This can lead to fraud, data theft, and brand damage, making runtime protection and tamper detection essential for Android and iOS applications.